⌘
Android & Mobile Security
APK analysis, application components, secure storage, network configuration, authentication and mobile-to-API trust boundaries.
OWASP MASVSAPK analysisPython
APPLICATION SECURITY & SOFTWARE ENGINEERING
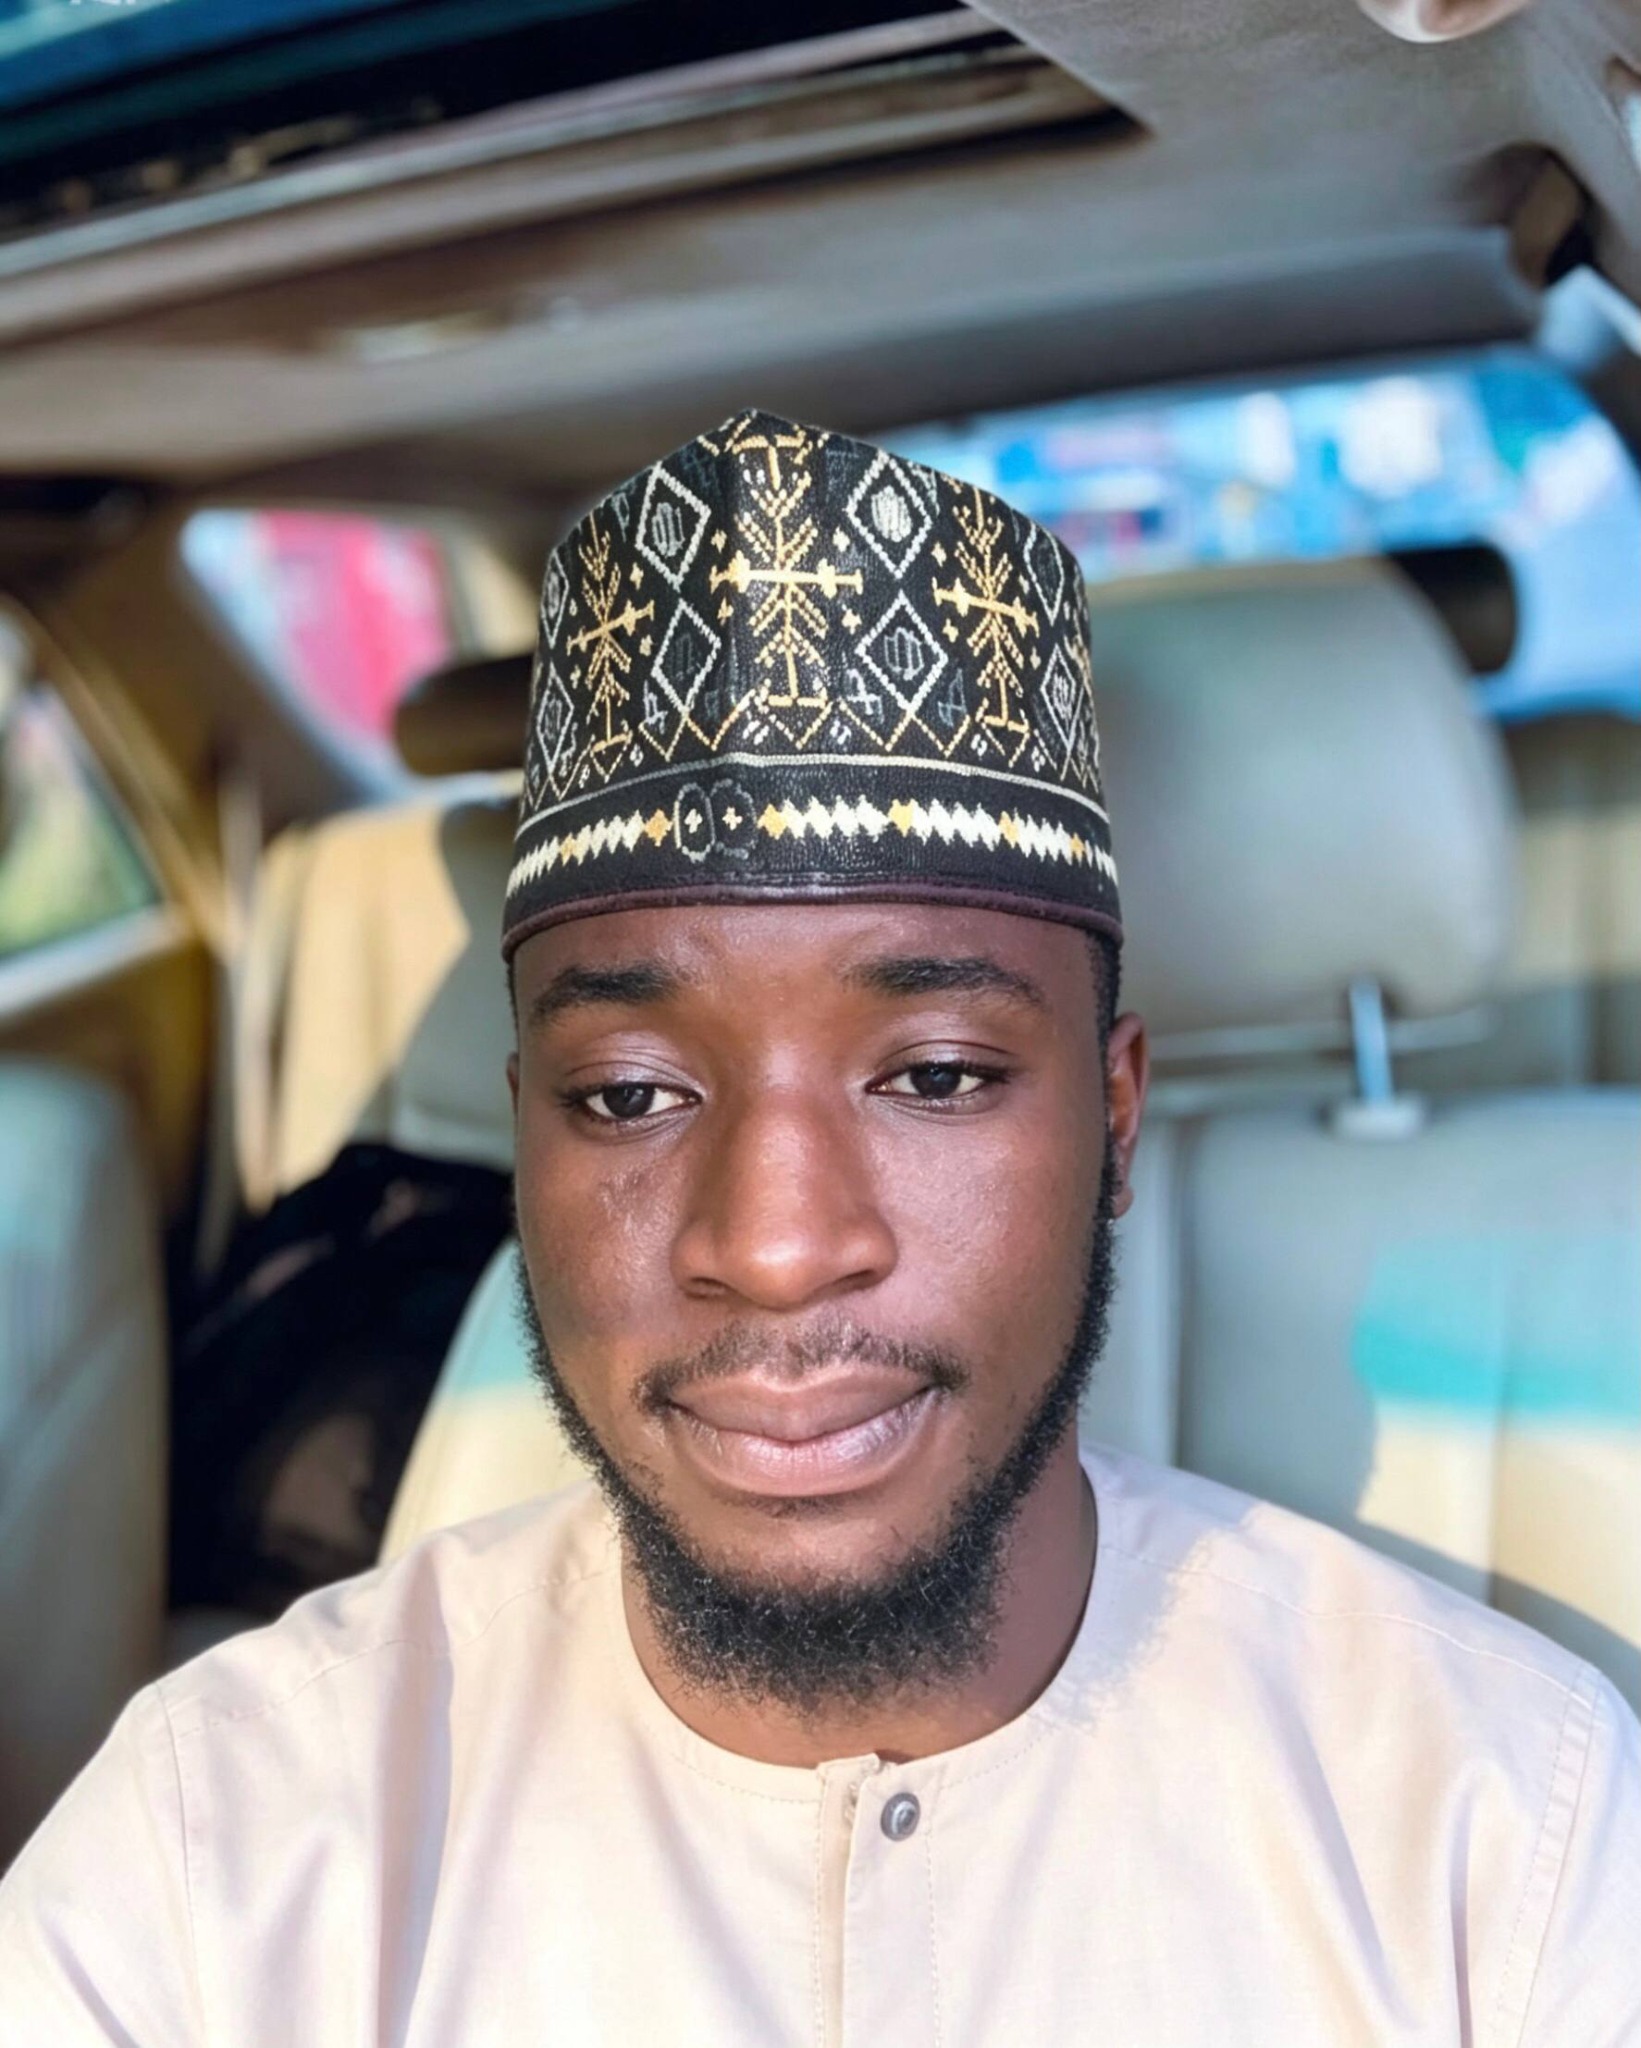
I'm Ahmad Ibrahim, an Android and web application security researcher, penetration tester and software builder. I turn ideas into working systems, examine their attack surfaces and help teams reduce real-world risk.
01 / ABOUT ME
I work at the intersection of product engineering and application security. My focus is designing useful software, testing its trust boundaries and building evidence-based improvements.
My practical work spans Android applications, API authorization, secure authentication, cloud-connected services and developer tooling. I use authorized labs and owned projects to explore weaknesses, validate fixes and communicate findings clearly.
I value reproducible evidence, maintainable code and accurate descriptions of every release. Research hypotheses are not confirmed vulnerabilities, and the published software is presented according to its verified capabilities.
02 / WHAT I DO
Practical skills across development, testing and remediation — not a list of unverified claims.
APK analysis, application components, secure storage, network configuration, authentication and mobile-to-API trust boundaries.
Authorized testing of session flows, object-level authorization, access control, data exposure and business-logic weaknesses.
Cross-platform products, backend services, database-backed workflows and testable customer/provider experiences.
Business workflow automation, evidence-oriented security tooling, release gates and human-controlled AI integrations.
03 / SELECTED WORK
A curated portfolio of engineering projects, research tools and early-stage products. Status labels reflect the verified development or release state.
A full-stack services platform connecting customers and providers through requests, bookings, messaging and secure account workflows. Explore its connected Android application and backend engineering.
An evidence-first Android application security CLI for APK analysis, reproducible observations and practical remediation guidance within authorized assessments.
An intelligent business platform connecting secure workspaces, governed automation and AI-assisted workflows to real organizational operations.
A research operations system for authorized scope management, evidence integrity, reproducible validation, triage and remediation verification.
An offline-first Quran and worship experience designed around trustworthy content, accessible study and dependable mobile use, with source and device assurance central to development.
A Nigeria-first marketplace combining group-buying discovery, merchant trust and transparent installment-shopping journeys, with financing dependent on compliant partnerships.
A digital-first eSIM telecommunications venture exploring device readiness, private subscriber journeys and accessible mobile service onboarding.
A privacy-conscious document platform being developed around PDF organization, conversion, optimization, security and intelligent workflows. Product architecture and safeguarded development automation form its engineering foundation.
Showing all 8 projects.
SECURITY RESEARCH
I investigate security vulnerabilities in mobile apps, web platforms and APIs with proper authorization, document reproducible evidence, and provide clear remediation guidance. My focus is on practical findings and fixes that help make software safer.
04 / PUBLISHED SECURITY RESEARCH
The Ahmad-IB Security Research Journal documents technical methods, source-backed engineering work and sourced intelligence, with clear limits on what has been demonstrated.
FEATURED ENGINEERING CASE STUDY · 26 OCT 2026
A technical explanation of report determinism, evidence handling, redaction and manual validation in the Android Security Toolkit. The article references public source code and tests without claiming a confirmed exploited vulnerability.
Research notes are not equivalent to acknowledged vulnerability disclosures. Claims are supported by cited material and limited to the work described.
04 / ACCESS TO PROJECTS
Application packages, implementation files and repository access are shared privately with approved collaborators.
ANDROID & BACKEND
OneCall is a customer and provider services platform. Application packages and backend materials are provided through an approved access process.
APPLICATION SECURITY ENGINEERING
Research tooling, implementation materials and technical documentation are shared privately where appropriate.
05 / THE PROCESS
A consistent cycle that connects functional software development with application security.
Clarify the business goal, assets, requirements and authorized scope.
Build maintainable components, data boundaries and usable interfaces.
Exercise failure modes, access controls and security-sensitive workflows.
Document evidence, fix weaknesses and verify regressions.
END-TO-END DELIVERY
A practical workflow for thoughtful engineering, accountable testing and ongoing improvement.
Clarify objectives, user needs, system boundaries and acceptance criteria.
Define delivery milestones, technical scope, resources and key risks.
Shape usable interfaces, information architecture and visual consistency.
Structure maintainable application components, integrations and data flows.
Develop and integrate mobile, web, API and automation capabilities.
Check user journeys, quality, security controls and regression behaviour.
Monitor, improve and support products through their operational lifecycle.
LEARNING & PROFESSIONAL PRACTICE
Security education and practice include EC-Council University studies, Cisco Networking Academy training, authorized testing labs and project-based engineering. Specific certificate documents can be added only when verified and approved for publication.
06 / GET IN TOUCH
Let's discuss a mobile app, a security assessment, an API review or an ambitious new product. For security testing, all work is scoped and authorized in advance.